
Technology now shapes how organisations operate, communicate and deliver their services, and that dependence has changed how businesses think about risk. Digital systems, data and technology infrastructure sit at the centre of daily work, which means a cyber incident is no longer a problem that stays inside the IT department. Preparing for one, and recovering from one, has become part of managing the business itself. This is why cyber resilience has become a serious part of how organisations plan for risk.
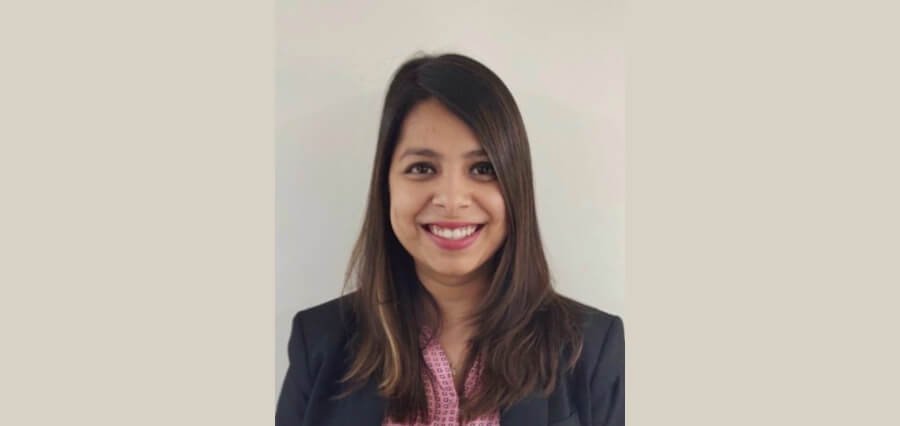
Evaa Saiwal, Practice Head of Liability & Cyber Insurance at Policybazaar for Business, works at the point where liability, cyber risk and insurance meet. Her work helps businesses understand exposures that are complex and always changing. She brings technical understanding, practical risk assessment and a close focus on the client’s business to that task, and she stresses the importance of having the right support in place when an incident actually strikes.
From Emerging Risk to Business Resilience
Evaa entered the insurance industry in the mid-2010s, when Cyber Insurance was still a relatively new product and was only beginning to evolve. What drew her in was its position at the intersection of insurance, technology and emerging risks. It was a subject where, in her words, “there was always something new to learn.”
She has watched the understanding of cyber risk change considerably since then. In the early years, the conversation centred largely on data breaches, and it was often seen as an IT issue. Where the discussion once stopped at the breach itself, it now extends to the wider effects on the organisation. Today she sees cyber clearly as a business risk. An incident can disrupt operations and affect revenue, customers and vendors. It can bring regulatory consequences, and in the end it can reach the balance sheet.
That shift has changed what Cyber Insurance means. It has moved from being a niche, technical product to an important component of overall business resilience.
Building a Team Around Learning
Because cyber keeps changing, Evaa believes continuous learning has to be part of her team’s culture. Technical knowledge matters, but she is clear that it is not enough on its own. When she looks for people to join the team, she looks for those who understand the client’s business, who can simplify complex risks and who can explain insurance in a practical way.
The real test, she says, comes when something actually goes wrong. A cyber incident can become a genuine crisis. Systems are down, customers are affected, and management is under pressure. At that point, clients need a team that is technically capable and empathetic, and one that is willing to step up. Sometimes that means coordinating several stakeholders at once. Sometimes it means being available at odd hours.
For Evaa, the combination of curiosity, technical capability and empathy is what changes the role her team plays. It is what takes them from being an insurance placement team to becoming a genuine risk partner. In that sense, the team is measured not only by what it knows, but by how it shows up when a client is under pressure.
Looking Beyond the Policy
Evaa helps clients see Cyber Insurance as part of their wider risk strategy by explaining it through what actually happens during an incident. Take a ransomware attack. The immediate questions have little to do with the insurance payout. They focus on containing the attack, determining whether data has been compromised, restoring operations, and managing obligations to regulators and customers.
A well-structured policy can support that response. It can provide access to forensic experts, legal advisors, and crisis-management and recovery specialists, along with financial protection for covered costs and for business interruption.
She is clear about the role insurance plays. Insurance, she says, “can significantly influence how effectively a business responds and recovers.” That is why she encourages clients to view it alongside cybersecurity controls, business continuity and incident-response planning. The aim is not simply to hold a policy that pays a claim. It is to know who to call, what to do next, and to have the right financial and technical support in place.
Starting With the Business
When Evaa assesses a client’s cyber risk, the starting point is never the insurance proposal. “We start with the business,” she says. Two companies with similar revenues can carry very different cyber exposures, depending on what they do, the data they hold and how dependent they are on technology.
Her team looks closely at the criticality of systems, sensitive data, cloud and third-party dependencies, previous incidents and the potential impact of downtime. They also assess the controls in place, including multi-factor authentication, endpoint protection, backups, access controls and employee training, and they check whether the incident-response plan has been tested.
All of this feeds into the final insurance structure, which reflects the client’s specific exposure. For a technology-dependent business, business interruption cover may be critical. A company holding significant customer data may need to give more weight to privacy and regulatory exposures. Businesses that rely on technology providers need to pay closer attention to dependent business interruption and supply-chain risks.
Seen this way, one product cannot suit every client, because each business is exposed in a different place. The objective, as Evaa describes it, is to build a programme around the place where a cyber incident could hurt that particular business the most, rather than to offer an off-the-shelf policy.
Keeping Pace With Emerging Threats
Among today’s threats, ransomware remains a major concern for Evaa. A single incident can set off several consequences together, including business interruption, recovery costs, data compromise and regulatory issues.
She also sees AI changing the nature of phishing, impersonation, deepfakes and social-engineering attacks. At the same time, growing dependence on cloud providers, software platforms and other technology partners is widening third-party exposure. An incident within that wider ecosystem can affect a business even when its own systems remain secure. Taken together, these developments mean a company can be affected by events that begin well outside its own walls.
For Cyber Insurance, the implication is that solutions cannot be designed only around the risks understood today. The industry needs to monitor emerging threats continuously, identify potential coverage gaps, and evolve products and policy wordings as quickly as the risk itself changes.
Technology is also changing how that risk is assessed. Underwriting once relied heavily on the information clients provided through proposal forms and questionnaires. Insurers can now supplement that with external vulnerability data, past loss patterns, industry benchmarks and other technology-driven insights, which makes underwriting more dynamic and better informed. In other words, insurers can now look at a client’s risk through a wider lens than the answers on a form. AI and data analytics can also surface patterns and potential areas of concern that traditional underwriting may not make visible.
Evaa is quick to add a limit. “Technology does not replace human judgement,” she says. What it does is give underwriters and risk professionals better information to understand and price risk. So while technology is creating new cyber risks, it is also becoming an important tool for assessing them more effectively.
Preparing Before an Incident
For Evaa, preparation begins with recognising that cyber risk can touch any organisation, however strong its systems may be. That changes the questions a business should ask. Wondering how to prevent an attack is not enough. Businesses also need to ask how prepared they are to respond if something happens. Prevention, however well done, cannot be the only plan.
Answering that means having strong cybersecurity controls, regular employee training and an incident-response plan that has been tested. The training should reach beyond IT. Management, legal, finance, communications and HR all need to understand their roles during an incident.
Evaa points to recent large-scale incidents, including the cyberattack affecting Jaguar Land Rover, as a reminder that even sophisticated organisations can face significant disruption. Strong controls remain essential, but organisations also need resilience that goes beyond prevention.
Insurance cover is part of this preparation, and it should be understood before a claim occurs. Businesses should know what needs to be notified, what specialist support is available and how the response process works.
Evaa sums it up simply. “Strong cyber resilience comes from three things working together,” she says: good cybersecurity, a well-prepared organisation and the right insurance programme.
Balancing Coverage and Cost
On the question of cost, Evaa looks past the price tag. Two insurers can offer the same limit while providing very different levels of protection, so the premium cannot be the only measure.
That is why her team looks closely at the technical nuances of policy wording. They examine deductibles, business interruption triggers, third-party and outsourced service-provider exposures, cloud infrastructure and other specific coverage definitions.
These details decide how a policy behaves when it is actually needed, and several practical questions come up. Does business interruption respond when a company voluntarily shuts down to contain an incident? How is dependent business interruption covered? Do cloud environments such as SaaS, IaaS and PaaS fall within the relevant definitions? And how are emerging exposures such as impersonation fraud, telephreaking, clean-up costs and privacy liability addressed?
Affordability still matters. Evaa works with clients to structure appropriate limits and deductibles within their budget. As she puts it, “Clients should compare policies based on how they will actually respond during a claim.”
A More Continuous Partnership
Looking ahead, Evaa expects Cyber Insurance to become a continuous partnership between the insured, the insurer and the broker, rather than an annual insurance transaction.
The reason is simple. Cyber risk does not stay unchanged for twelve months. Technology changes, businesses adopt new systems, vulnerabilities emerge, and attack methods evolve. Each party has a part to play. The insured needs to keep strengthening controls and understanding new exposures. Insurers need to evolve their underwriting and coverage. Brokers need to connect changing business risks with appropriate insurance solutions.
She expects the conversations between them to cover emerging threats, claims trends, technology changes and whether existing protection remains adequate.
Evaa puts it plainly. “Stronger cyber resilience will come from shared responsibility,” she says. The insured, insurer and broker will keep learning from each other and growing together as the risk grows.
Staying Curious in a Field That Keeps Evolving
Evaa’s advice to aspiring professionals, especially women, who want to build careers in Cyber Insurance and risk management starts with a single idea: stay curious, and do not be intimidated by how technical the subject may seem at first. Nobody needs to know everything from day one. Strong fundamentals, continuous learning, asking questions and gaining experience across different risks and claims are what build expertise.
She finds cyber particularly exciting for young professionals because it is still evolving. New technologies, regulations and threats are constantly creating opportunities to learn and contribute to the industry.
For women in particular, her message is not to wait until they feel completely ready before entering a technical conversation or taking on a bigger role. She encourages them to prepare well, build depth and have the confidence to participate. “Expertise is something you build over time,” she says.
Evaa also offers a way to look at the pace of the field. That it never stops presenting something new is not a disadvantage in cyber risk. In her view, it is one of the biggest opportunities.